Your internet feed, let us censor it

So who really thinks giving BT et all control over what you can see on the internet is a good idea:

Four leading web providers are to offer customers the option to block adult content at the point of subscription, the BBC understands.

BT, Sky, Talk Talk and Virgin will offer the protection for smart phones, laptops and PCs.

It comes as David Cameron is set to meet industry representatives amid concern over sexualisation of children.

The prime minister will also launch Parentport – a website to help parents complain about inappropriate content.

And he will back a ban on billboards displaying risque images near schools.

The new measures, aimed at helping parents protect their children from internet porn and other explicit sites, follow a report earlier this year by the Mothers’ Union charity.

It’s all part of the further childproving of society, where anything that potentially could be seen by children and “harm” them has to be packed off to some adults only ghetto. And the internet, being the newest, biggest and still scariest medium available to children of course has to be controlled the most. But you’d be stupid as parents to trust Sky or Virgin with making your internet feed child safe. If these filtering efforts are to be effective they have to be draconian, filtering out anything that talks about s*e*x* or mentions a naughty word — so much for Scunthorpe — and taking a lot of false positives down too. Sex education sites, rape support centres, GLBT blogs, those are all vulnerable to such filtering, because all too often already they’re blocked by net nanny software.

Either that or this sort of filter will be wholly ineffective and consist of only a token effort to block playboy.com… Remember, for these internet providers, this is just an added cost so they’ll be looking to do it as cheaply as possible.
The Netherlands embraces net neutrality

Imagine a world without net neutrality

Dutch politicians as a class are not know for their internet nous, but they exceeded expectations in a big way this week. Lately several big mobile phone companies (ex government monopoly KPN and of course Vodafone) have been whinging about their consumers not texting and phoning enough. Instead people have increasingly turned to things like WhatsApp or Skype to do it for free, over mobile internet. And sure, KPN and Vodafone earn money selling mobile internet subscriptions, but not enough. Which is why KPN announced a few weeks ago it would start to charge extra for access to certain kinds of internet services.

Which pissed people off big time, of which politicians took notice and last week the opposition parties drafted a proposal to introduce net neutrality, which would prohibit providers from filtering or charging for access to internet services the way Vodafone and KPN wanted to. If this proposal makes it into law, the Netherlands would be one of the first countries in the world to regulate internet access this way. Which is important, because it means your provider will no longer be able to decide what you can and cannot see on the internet.

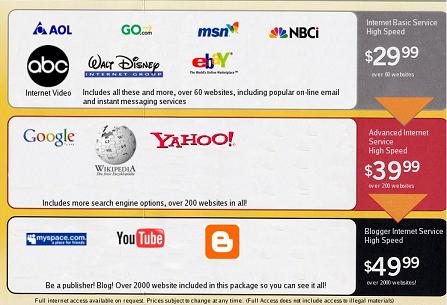
Without net neutrality, we’d see mobile internet evolve cable access subscription schemes: you’d just get a small part of the internet with your standard subscription and would have to pay extra to see the more interesting stuff, without ever having the opportunity to see everything, a bit like on the illustration above. Kudos for our politicians for preventing this from happening.

Of course not

Alex asks whether politicians learned anything from the News of the World phone hacking scandal:

Also, did the central government have any communications security at all? Did CESG or MI5 not have anything at all to say about this? Didn’t any of them just change their damn password, or even change their damn number?

Of course not. As a class politicians are the group most clueless about ICT and worst placed to make decisions on anything to do with it and that gets worse the higher up the ranks you get. Most modern politicians these days have never been anything but politicians and in that job you only need a pc as a glorified typewriter, while once you get high enough on the ladder the normal computer scutwork most of us have to deal with day to day can all be fobbed off on interns who’ll print out all the important documents for you. So I doubt they’ve spent any time at all thinking about communications security.

Case in point: several Dutch politicians got hit with a variant of what the News of the World did recently, as investigative reporters from the newsshow Één Vandaag “hacked” their voicemails by trying the standard Vodaphone pincode on them. Quite a few ministers turned out not to have bothered resetting this or even knew that they had to do that. Worse, neither did their IT department. Personally I think having voicemail at all is way too much of a security risk anyway and I’d switch it off altogether if I were in such a responsible function, but than that’s too much of a hassle.

What doesn’t help either is that is how much party political business is interwoven with government responsibilities for modern politicians, meaning that there’s a high risk for cross pollution anway. In an ideal world government ministers would have two or three separate mobiles: one for their job, one for journalists and party workers to reach them on and another for the family, but I suspect most people use the same phone for everything…

What a porn ban would also do

Make it that much harder for transgender teens to get support:

Yes, they exist. I hated what I was for nearly all my teenage years., wanting to rip the skin from my body, sobbing myself to sleep at night because I couldn’t understand what I was. But then came along the internet. Oh, the internet. It fucking saved me. It gave 18 year old me a view of the world that made me realise that I wasn’t alone, that I could do something about the pain that made me want to die.

Claire Perry, and her evil piece of legislation, would take that lifeline away. Oh, maybe not conciously. I doubt she even knows that trans people exist, let alone that there are trans teenagers out there who rely on the internet for vital support. She wouldn’t notice as the sites they use to gain crucial advice from are blocked, due to having never-quite-defined “adult materials”, as support channels are closed down for “endangering youth”. She wouldn’t notice as sites all over the net are blocked for containing mention of sex, genitals, puberty and sexuality, when what they are doing is educating a badly unrepresented and unsupported section of society.

Not that such a scheme, as proposed by some daft British MP, would actually work in the real world anyway, but it could do quite a lot of collatoral damage anyway. Worse, any such scheme is going to disproportionally hurt self help sites and support sites rather than truly exploitative sites, because the former are always going to be easier to find and shut down.

Security is overrated

Charlie Stross has made a little list of where computer science went wrong:

I’m compiling a little list, of architectural sins of the founders (between 1945 and 1990, more or less) that have bequeathed us the current mess. They’re fundamental design errors in our computing architectures; their emergent side-effects have permitted the current wave of computer crime to happen …

Let’s not quibble about the examples Charlie gives, but assume that he is right to say that these are what makes computer crimes of all sort possible. But does it matter? Or should we just look at computer crime as an unfortunate cost of actually being able to do something useful with computers? Of the six specific “sins” Charlie mentions (von Neumann architecture, String handling in C, TCP/IP lacking encryption, The World Wide Web, User education and Microsoft) at least three are the way they are because that’s what made them useful in the first place. Von Neumann architecture, where data and code are stored in the same memory and can be freely mixed made it much easier to program computers, hack them to do all kinds of tricks and squeeze the most out of limited means — not so important now perhaps, but very important even a few decades ago. TCP/IP being simple and largely unsecure makes it easy to setup and use; it’s a “good enough” solution to the problem of coupling disparate computers and networks together. The World Wide Web is again something that worked from the start and could evolve itself towards ever increasing complexity, as the hackability that does make it vulnerable to attack also meant it could be extended quite easily to scale up and deal with new demands.

Even Microsoft, evil as it is and crappy as much of its software still remains, is the way it is because it has consistently tried to give people useful hacks rather than properly designed vapourware. Ironic as it is, I’ve always had the sneaking suspicion MS DOS and Windows did as well as they did because they were so open and easy to hack around in compared to their competitors.

As Charlie admits, the most secure mainstream computer today is perhaps the IPad, in which basically you can only do what Steve Jobs allows you to do: a consumer device like your television more than a real computer. Any fule knows that security comes at the expense of usability: the more secure a computer the less you can do with it, certainly the less you can use it in unexpected ways. The other side of the medal is that with increased freedom comes greater vulnerability.

On the other hand, even if the right choices had been made way back when, does anybody doubt that with our reliance on computers and the internet in our daily lives and businesses, computer crime would be any less? You use something, it will be abused.