Not sure what to think about this

The Washington Post looking into the data sets Google uses to train its chatbots and some surprising results popped up:

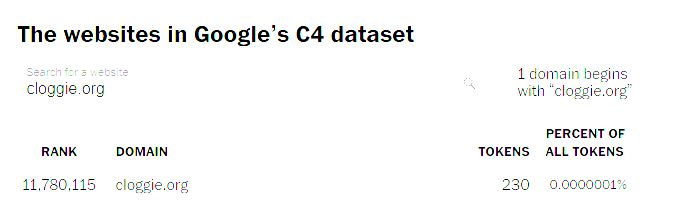
A screenshot from the article showing cloggie.org is present in the data set with 230 tokes and rank 11,780,115

As The Post put it:

To look inside this black box, we analyzed Google’s C4 data set, a massive snapshot of the contents of 15 million websites that have been used to instruct some high-profile English-language AIs, called large language models, including Google’s T5 and Facebook’s LLaMA. (OpenAI does not disclose what datasets it uses to train the models backing its popular chatbot, ChatGPT)
The Post worked with researchers at the Allen Institute for AI on this investigation and categorized the websites using data from Similarweb, a web analytics company. About a third of the websites could not be categorized, mostly because they no longer appear on the internet. Those are not shown.
We then ranked the remaining 10 million websites based on how many “tokens” appeared from each in the data set. Tokens are small bits of text used to process disorganized information — typically a word or phrase.

Because the article kindly included a search bar I found out my website is also included in the data set, with some 230 tokens. It would be interesting to see what exactly was included in those 230 tokens from the more than two decades of rambling contained in this site. Sadly, that’s not provided here. Nevertheless, an interesting look in the data used in training socalled AI programmes and its limitations.

Hack into the mooframe

So much for all those visionary cyberpunk authors of the eighties and nineties. They never so much as hinted that in the 21st century, the brave new hacking elite would consist of Nebraska farmers desparate to repair their John Deere tractors:

Not to be too disparaging, it’s hard to predict things, especially the future. But still. Reading that American farmers are buying Ukrainian software to hack their tractors really gives me the feeling of living in one of Bruce Sterling’s novels, which is not necessarily a good thing…

Stupid internet connectivity bug #firstworldproblems

So I’ve been having an annoyingly stupid connectivity bug the last day or so, where when I click on a link my browser starts thinking to itself, then gives me an error message that the site ain’t available. Then, when I try again, up it pops. This happens intermittedly, even on pages I just visited and in both Opera and IE. It doesn’t matter whether I connect to my router through ethernet or WLAN, whether both are used or not and doesn’t seem to happen on my other, laptop computer running Vista (work made me use it, don’t judge me.) My own computer is running Windows 7/64 bits. For one glorious moment I thought it could perhaps be the fake LAN network Oracle VirtualBox needs to have internet access, but disabling that didn’t help either.

Any ideas?

(Windows 7 is decent enough as an operating system when everything works, but once something goes wrong it’s pulling teeth to find out what the fsck is going on. Everything is so locked down and hidden from the user’s view and gets in your way when you’re bug tracking.)

You wouldn’t steal the music for your anti-piracy ad


Dutch copyright advocacy group BREIN asks composer Melchior Rietveldt to create the music for an anti-piracy ad to be shown at a local film festival. That’s in 2006. A year later Rietveldt notices that his music is used in another piracy ad, one put on dozens of dvd titles in the Netherlands:

The composer now claims that his work has been used on tens of millions of Dutch DVDs, without him receiving any compensation for it. According to Rietveldt’s financial advisor, the total sum in missed revenue amounts to at least a million euros ($1,300,000).

The existence of excellent copyright laws and royalty collecting agencies in the Netherlands should mean that the composer received help and support with this problems, but this couldn’t be further from what actually happened.

Soon after he discovered the unauthorized distribution of his music Rietveldt alerted the local music royalty collecting agency Buma/Stemra. The composer demanded compensation, but to his frustration he heard very little from Buma/Stemra and he certainly didn’t receive any royalties.

It gets better:

Earlier this year, however, a breakthrough seemed to loom on the horizon when Buma/Stemra board member Jochem Gerrits contacted the composer with an interesting proposal. Gerrits offered to help out the composer in his efforts to get paid for his hard work, but the music boss had a few demands of his own.

In order for the deal to work out the composer had to assign the track in question to the music publishing catalogue of the Gerrits, who owns High Fashion Music. In addition to this, the music boss demanded 33% of all the money set to be recouped as a result of his efforts.

So an anti-piracy group doesn’t ask permission or pay a composer to use his music and the group that should be protecting his rights actually has its boardmembers attempt to extort him…

The future of the internet according to CmdrTaco

MetaFilter founder Matt Haughey interviews Slashdot founder Rob “CmdrTaco” Malda, who is not optimistic about the future of the internet:

Rob: The internet is simply not as free as it was when Slashdot began. Government is increasingly legislating away our rights and criminalizing actions that are impossible to regulate. I know it’s inevitable, but it’s still disappointing to witness. The joy of logging in to an IRC chat room in the early 90s, to talk to people who were innovating powerful technologies simply for the sake of it was absolutely intoxicating. To be able to talk to the guy who was responsible for some component of your system. We were all pseudo-anonymous strangers brought together by the technology that we loved, and the belief that an open future was spread out before us. The future will be exciting for my children, but I’m afraid that their technology will come in boxes welded shut at the factory. Their software locked down. Linux, and the Internet broke everything wide open. It’s taken 20 years to get a lot of it boxed back up again. I hope there are still air cracks by the time my kids are old enough to jam screwdrivers in there.

On the other hand, there’s the experience of MetaFilter commenter dreamyshade of working on the Ipad/Iphone hacking scene:

One of my favorite parts of working on Cydia is when I meet young kids who know exactly what jailbreaking is and how to do it. (Like at Thanksgiving, telling acquaintances what I work on — the 12-year-old boy grinning in surprised recognition while the grown-ups carefully listened to an explanation of the concept.) There are lots of kids splashing around on their hand-me-down iPod touches jailbroken in one way or anoher: installing goofy homebrew software, crafting custom icon themes with terrifically ugly icons, installing OpenSSH and forgetting to change the default password but learning to SSH in and paste intriguing commands from the internet, editing plists to enable hidden features, figuring out how to restore the device when things inevitably go wrong, and generally making a lively mess of the device they get to totally play with. They cause some support burden for Cydia and App Store developers alike, but this is one way to learn to feel comfortable with poking around at the internals of things, to gain the confidence to break stuff because you know you can figure out how to fix it, to self-identify as a person good with technical stuff, to take an interest in AP Computer Science class later. This makes me happy. Each new generation of devices gets harder to jailbreak, but for now there’s still some good stuff happening.

I hope dreamyshade is right but I fear CmdrTaco is closer to the truth. Internet has long ago ceased to be the domain of hardcore geeks — nothing wrong with that — but with it has come the Facebooking of the internet, where you sacrifise your freedom and privacy for ease of use and comfort.